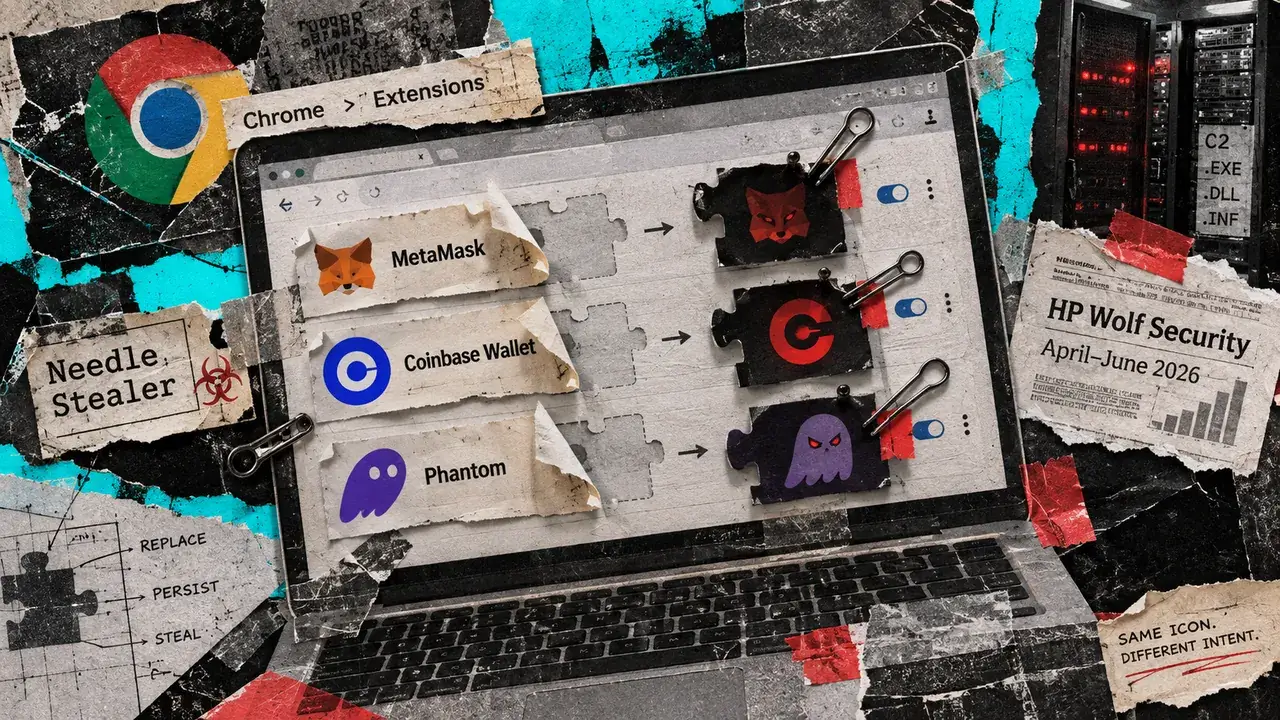
Fake AI crypto advisor swaps wallets in browsers
- —The malware searched for extensions by 32-character ID: MetaMask, Phantom, Trust Wallet, Coinbase Wallet, OKX, Tonkeeper
- —A signed OLEView bypassed SmartScreen, with the payload hidden in the DLL iviewers.dll
- —The replacement extension connected to a C2 server and harvested logins and passwords via fake screens
- —HP did not disclose the number of victims or the amount of funds stolen
Why it matters: The attack targets the most popular wallets through legitimate signatures and ads, so users should verify extensions and avoid running third-party 'AI traders'.
Source: CryptoSlate