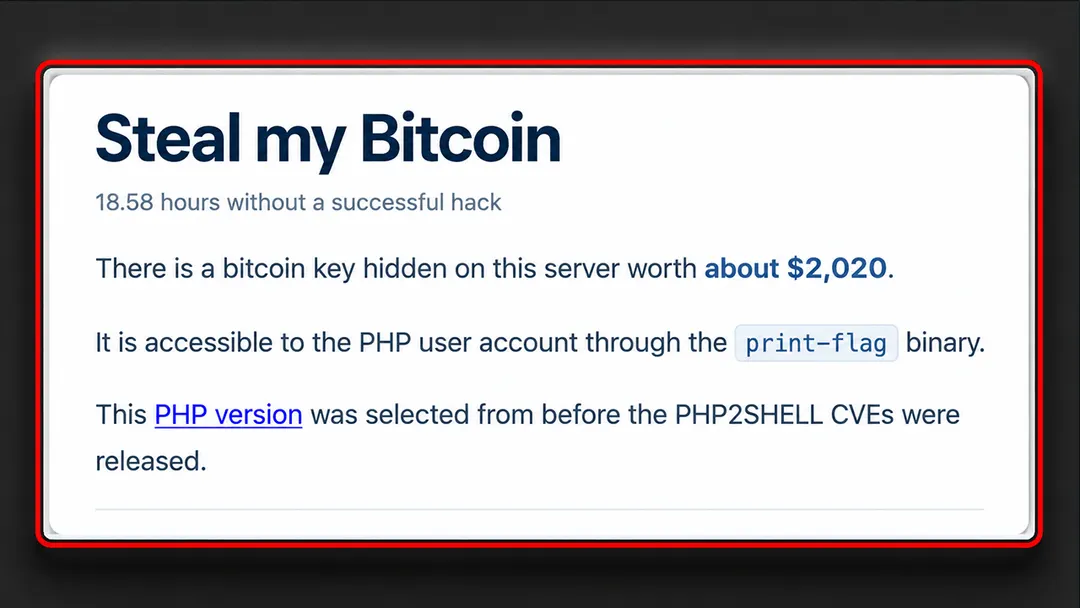
Steal My Bitcoin Bounty Unclaimed After 17 Hours as Researcher Questions Server Setup
- —Bounty grew from $500 to about $2,000 (0.025 BTC) via donations
- —Wallet stayed untouched for more than 17 hours after launch
- —PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 carry severity scores of 9.2
- —Patches for PHP 8.4.26 shipped Oct. 21, but the site's config may block exploitation
Why it matters: The case shows how a server misconfiguration can neutralize a real vulnerability — and raises questions about whether such bounty challenges are run in good faith.
Source: Bitcoin.com
More on this
Regulation · Oct 13ARK Research Director: 70% of Adviser Questions Are About Quantum, Not Token Revenue
Security · Sep 21RAT malware steals over $235,000 in crypto from hundreds of victims in 48 hours
Security · Oct 22Cysic offers attacker 10% white-hat bounty to return 275.872 ETH within 72 hours