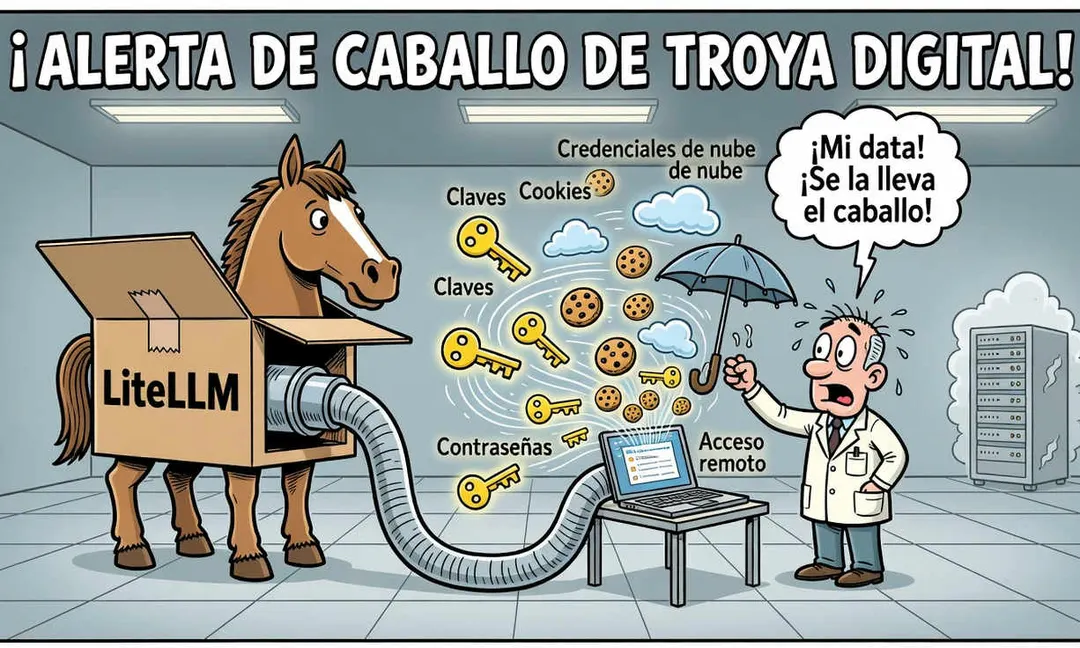
Malicious LiteLLM 1.107.0 stole cloud credentials and AI API keys
- —Version 1.107.0 was published on Oct. 21, 2026 and removed from PyPI; Docker images stayed infected
- —A 16-module stealer targeted AWS, GCP and Azure credentials plus OpenAI, Anthropic and Cohere API keys
- —A RAT polled attacker infrastructure hourly, enabling remote command execution
- —Stolen data was AES-256-CBC encrypted and sent to the litellm.dev domain
Why it matters: LiteLLM sees roughly 23 million weekly downloads, so leaked cloud and AI keys could expose infrastructure at many organizations.
Source: DiarioBitcoin