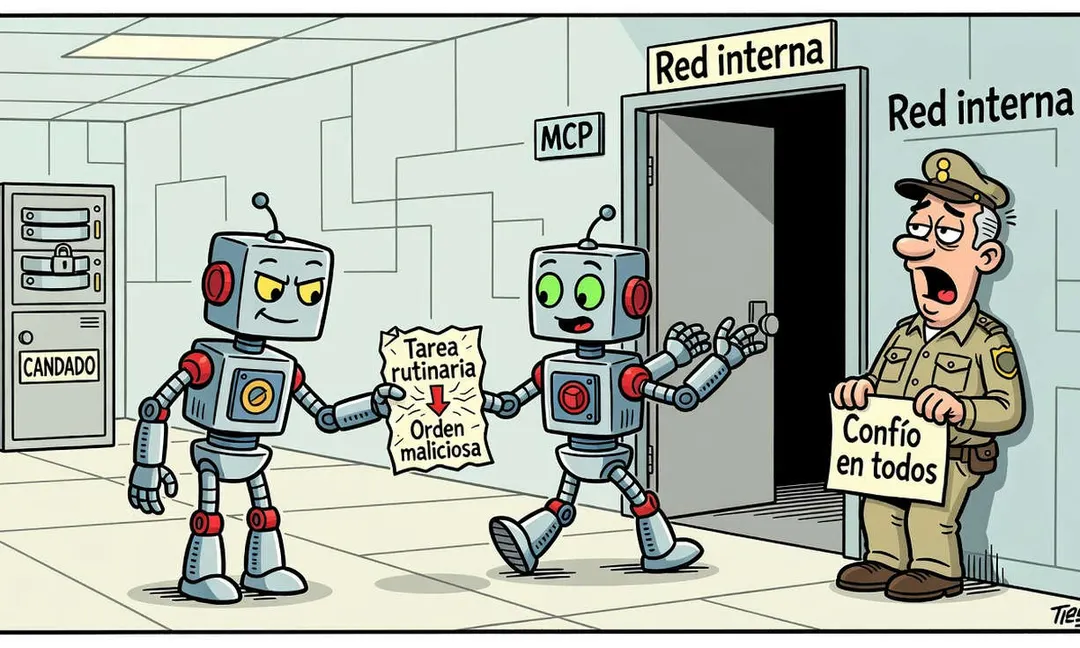
MCP flaws let attackers propagate exploits between AI agents
- —Google fixed an 8/10 severity flaw in MCP Toolbox for databases
- —Rapid7 patched CVE-2026-97228 rated 2.7/10 in Bulk Export MCP
- —The 'protocol pivoting' attack exploits trust between MCP and A2A
- —Agents at Google, JPMorgan, Weaviate, Rapid7 and government bodies were tested
Why it matters: As AI agents spread across crypto infrastructure, MCP trust chains become a new attack vector for wallets and protocols.
Source: DiarioBitcoin